New Standards Will Protect Encryption From Quantum Computers

From our bank accounts to smartphones, all our sensitive data and devices are protected with a technology known as cryptography.

Present-day cryptography essentially uses a very challenging set of math problems that are nearly impossible for current computers to solve. These math problems act as a “lock” to keep hackers or spies away from the personal information in your “house.”

But experts are working to develop specialized machines known as quantum computers. Quantum computers have incredible potential to do tasks that current computers struggle with, such as discovering new medications.

The downside is that they may also have the potential to thwart today’s cryptography. Sufficiently powerful versions of these machines could put all our personal information, financial transactions, and business and government secrets at risk.

READ MORE

Announcing Final NIST Transit CSF Community Profile + Upcoming Webinar

The NIST National Cybersecurity Center of Excellence (NCCoE) has released the final NIST Interagency Report 8576, Transit Cybersecurity Framework Community Profile, to help U.S. transit agencies strengthen their cybersecurity practices while supporting safe and resilient transit services.

Additionally, the NCCoE is hosting a virtual event on September 1, 2026 to discuss the Profile. Register today to reserve your spot and discover how the Transit Cybersecurity Framework (CSF) Community Profile can support your agency’s cybersecurity efforts.

Background

Transit agencies operate a complex network of business and operational technology (OT) systems to fulfill their mission. As these systems increasingly rely on digital, network-based communication, the cyberattack surface has expanded, requiring agencies to manage cybersecurity risks alongside safety and operational priorities.

Developed in collaboration with transit agencies, federal agencies involved in transit, and other stakeholders, the Transit CSF Community Profile provides a voluntary, risk-based resource to help transit agencies strengthen cybersecurity preparedness and resilience against evolving threats facing the sector.

The Transit CSF Community Profile focuses on three strategic priorities:

  1. Securing and managing critical assets to support safe and reliable operations.
  2. Strengthening collaboration with stakeholders and suppliers to improve resilience and supply chain security.
  3. Continuously improving organizational operations and processes, workforce cybersecurity awareness, and capabilities.

The Profile helps transit agencies prioritize cybersecurity activities that align with their mission by mapping them to NIST Cybersecurity Framework (CSF) 2.0 outcomes and relevant industry guidelines and considerations.

Download the final Transit CSF Community Profile today to learn how it can support your organization’s cybersecurity efforts!

Upcoming Project Webinar

Join the NIST National Cybersecurity Center of Excellence (NCCoE) on September 1, 2026 at 2:00 P.M. EDT for a virtual event and panel discussion to learn more about the final Profile. Hear transit operators share their perspectives on the Profile and discuss how transit agencies can use it to strengthen cybersecurity and support safe, reliable, and resilient transit operations.

Visit the event page and register today!

View the Profile 

Upcoming Webinar: Foundational Cybersecurity for Small Businesses

Date: August 20, 2026

Time: 2:00 p.m.- 3:00 p.m. EDT

Description:

The small business community is a large portion of the U.S. and global economy and is also largely under-resourced when it comes to building strong cyber defenses. The efficient use, or prioritization, of limited resources is critical. Speakers from the Cybersecurity and Infrastructure Security Agency (CISA), Federal Bureau of Investigation (FBI), and National Institute of Standards and Technology (NIST) will share how to identify cybersecurity risks that small businesses commonly face and will share practical and actionable cybersecurity safeguards that can significantly reduce cybersecurity risks and that typically do not take significant time, financial investment, or technical expertise to implement.

Ample time will be saved for audience questions and discussion.

Speakers:

  • Colleen P. Ferranti, Assistant Section Chief, Cyber Engagement & Intelligence Section, Federal Bureau of Investigation (FBI)
  • Christine Serrano Glassner, Chief External Affairs Officer, Cybersecurity and Infrastructure Security Agency (CISA)
  • Daniel Eliot, Lead for Small Business Engagement, National Institute of Standards and Technology (NIST)
Register Here

CISA, FBI, and Partners Release Joint Cybersecurity Advisory on Gunra Ransomware

The Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI), in collaboration with U.S. government and international partners, released a joint Cybersecurity Advisory, #Stopransomware: Gunra Ransomware, part of an ongoing series detailing ransomware variants and threat actors. This joint advisory provides technical details on Gunra activity, along with detection and mitigation guidance to help protect at-risk organizations across government and critical infrastructure.

Gunra first emerged in April 2025 and expanded to a formal ransomware-as-a-service (RaaS) affiliate program advertised on dark web forums. Gunra actors use a double-extortion model, meaning actors both encrypt and exfiltrate sensitive data to create two forms of leverage for collecting ransom payments. They demand ransom via a Tor network-based negotiation portal and threaten to publish stolen data on their dedicated leak site (DLS) if victim organizations do not pay within five to seven days. As part of the 2026 expansion, Gunra actors have adopted branding aliases (including Golden Community) and further commercialized by actively recruiting penetration testers and ethical hackers as initial access brokers in exchange for a share of ransom profits. They have also demonstrated the ability to disable backup features, and in one instance, prevented restoration by deleting backup and archived data stored at both a primary data center and disaster recovery center. Victim organizations listed on Gunra’s DLS site are from multiple sectors across the world.

CISA, the FBI, and authoring agencies urge organizations to implement the advisory’s mitigations, including the following key actions:

  • Prioritize patching known exploited vulnerabilities in internet-facing systems, including virtual private network (VPN) gateways and remote desktop protocol (RDP)-exposed infrastructure.
  • Implement and test offline, immutable backups stored in a physically separate, segmented location to ensure recoverability without ransom payment.
  • Segment networks to restrict lateral movement from an initially compromised device to other systems in the organization.

Read the full advisory for more information on how to protect your organization from Gunra.

Multiple Vulnerabilities in Adobe Products Could Allow for Arbitrary Code Execution – PATCH: NOW

Multiple vulnerabilities have been discovered in Adobe products, the most severe of which could allow for arbitrary code execution.

*            Adobe Bridge is a powerful asset management tool that allows creative professionals to preview, organize, edit, and publish multiple creative assets efficiently across the Creative Cloud ecosystem.

*            Adobe Format Plugins are software add-ons used by Adobe applications to handle file formats, convert data types, and process specific file structures safely.

Successful exploitation of the most severe of these vulnerabilities could allow for arbitrary code execution in the context of the logged on user. Depending on the privileges associated with the user, an attacker could then install programs; view, change, or delete data; or create new accounts with full user rights. Users whose accounts are configured to have fewer user rights on the system could be less impacted than those who operate with administrative user rights.

THREAT INTELLIGENCE:

There are currently no reports of these vulnerabilities being exploited in the wild.

SYSTEMS AFFECTED:

*            Adobe Bridge 15.1.6 (LTS) and earlier versions

*            Adobe Bridge 16.0.5 and earlier versions

*            Adobe Format Plugins 2026.05 and earlier versions

RISK:

Government:

*            Large and medium government entities: High

*            Small government entities: Medium

Businesses:

*            Large and medium business entities: High

*            Small business entities: Medium

Home users: Low

TECHNICAL SUMMARY:

Multiple vulnerabilities have been discovered in Adobe products, the most severe of which could allow for arbitrary code execution. Details of these vulnerabilities are as follows:

Tactic: Execution (TA0002 <https://learn.cisecurity.org/e/799323/tactics-TA0002-/4w1hhf/2733627729/h/9-fk1zhPs62wccYt3ayhKzRTeyVr8siFCddDHpONOsY> )

Technique: Exploitation for Client Execution (T1203 <https://learn.cisecurity.org/e/799323/techniques-T1203/4w1hhj/2733627729/h/9-fk1zhPs62wccYt3ayhKzRTeyVr8siFCddDHpONOsY> ):

Adobe Bridge:

Untrusted Search Path (CVE-2026-48395, CVE-2026-48391) Incorrect Authorization (CVE-2026-48396, CVE-2026-48390) Improper Limitation of a Pathname to a Restricted Directory (‘Path Traversal’) (CVE-2026-48374) Out-of-bounds Write (CVE-2026-48392, CVE-2026-48393, CVE-2026-48394)

Adobe Format Plugins:

Heap-based Buffer Overflow (CVE-2026-48372)

Successful exploitation of the most severe of these vulnerabilities could allow for arbitrary code execution in the context of the logged on user. Depending on the privileges associated with the user, an attacker could then install programs; view, change, or delete data; or create new accounts with full user rights. Users whose accounts are configured to have fewer user rights on the system could be less impacted than those who operate with administrative user rights.

RECOMMENDATIONS:

We recommend the following actions be taken:

*            Apply the stable channel update provided by Adobe to vulnerable systems immediately after appropriate testing. (M1051 <https://learn.cisecurity.org/e/799323/mitigations-M1051/4w1hhm/2733627729/h/9-fk1zhPs62wccYt3ayhKzRTeyVr8siFCddDHpONOsY> : Update Software)

              *            Safeguard 7.1: Establish and Maintain a Vulnerability Management Process: Establish and maintain a documented vulnerability management process for enterprise assets. Review and update documentation annually, or when significant enterprise changes occur that could impact this Safeguard.

              *            Safeguard 7.2: Establish and Maintain a Remediation Process: Establish and maintain a risk-based remediation strategy documented in a remediation process, with monthly, or more frequent, reviews.

              *            Safeguard 7.6: Perform Automated Vulnerability Scans of Externally-Exposed Enterprise Assets: Perform automated vulnerability scans of externally-exposed enterprise assets using a SCAP-compliant vulnerability scanning tool. Perform scans on a monthly, or more frequent, basis.

              *            Safeguard 7.7: Remediate Detected Vulnerabilities: Remediate detected vulnerabilities in software through processes and tooling on a monthly, or more frequent, basis, based on the remediation process.

              *            Safeguard 16.13: Conduct Application Penetration Testing: Conduct application penetration testing. For critical applications, authenticated penetration testing is better suited to finding business logic vulnerabilities than code scanning and automated security testing. Penetration testing relies on the skill of the tester to manually manipulate an application as an authenticated and unauthenticated user.

              *            Safeguard 18.1: Establish and Maintain a Penetration Testing Program: Establish and maintain a penetration testing program appropriate to the size, complexity, and maturity of the enterprise. Penetration testing program characteristics include scope, such as network, web application, Application Programming Interface (API), hosted services, and physical premise controls; frequency; limitations, such as acceptable hours, and excluded attack types; point of contact information; remediation, such as how findings will be routed internally; and retrospective requirements.

              *            Safeguard 18.2: Perform Periodic External Penetration Tests: Perform periodic external penetration tests based on program requirements, no less than annually. External penetration testing must include enterprise and environmental reconnaissance to detect exploitable information. Penetration testing requires specialized skills and experience and must be conducted through a qualified party. The testing may be clear box or opaque box.

              *            Safeguard 18.3: Remediate Penetration Test Findings: Remediate penetration test findings based on the enterprise’s policy for remediation scope and prioritization.

*            Apply the Principle of Least Privilege to all systems and services. Run all software as a non-privileged user (one without administrative privileges) to diminish the effects of a successful attack. (M1026 <https://learn.cisecurity.org/e/799323/mitigations-M1026-/4w1hhq/2733627729/h/9-fk1zhPs62wccYt3ayhKzRTeyVr8siFCddDHpONOsY> : Privileged Account Management)

              *            Safeguard 4.7: Manage Default Accounts on Enterprise Assets and Software: Manage default accounts on enterprise assets and software, such as root, administrator, and other pre-configured vendor accounts. Example implementations can include: disabling default accounts or making them unusable.

              *            Safeguard 5.4: Restrict Administrator Privileges to Dedicated Administrator Accounts: Restrict administrator privileges to dedicated administrator accounts on enterprise assets. Conduct general computing activities, such as internet browsing, email, and productivity suite use, from the user’s primary, non-privileged account.

*            Restrict use of certain websites, block downloads/attachments, block Javascript, restrict browser extensions, etc. (M1021 <https://learn.cisecurity.org/e/799323/mitigations-M1021-/4w1hht/2733627729/h/9-fk1zhPs62wccYt3ayhKzRTeyVr8siFCddDHpONOsY> : Restrict Web-Based Content)

              *            Safeguard 2.3: Address Unauthorized Software: Ensure that unauthorized software is either removed from use on enterprise assets or receives a documented exception. Review monthly, or more frequently.

              *            Safeguard 2.7: Allowlist Authorized Scripts: Use technical controls, such as digital signatures and version control, to ensure that only authorized scripts, such as specific .ps1, .py, etc., files, are allowed to execute. Block unauthorized scripts from executing. Reassess bi-annually, or more frequently.

              *            Safeguard 9.3: Maintain and Enforce Network-Based URL Filters: Enforce and update network-based URL filters to limit an enterprise asset from connecting to potentially malicious or unapproved websites. Example implementations include category-based filtering, reputation-based filtering, or through the use of block lists. Enforce filters for all enterprise assets.

              *            Safeguard 9.6: Block Unnecessary File Types: Block unnecessary file types attempting to enter the enterprise’s email gateway.

*            Use capabilities to detect and block conditions that may lead to or be indicative of a software exploit occurring. (M1050 <https://learn.cisecurity.org/e/799323/mitigations-M1050/4w1hhx/2733627729/h/9-fk1zhPs62wccYt3ayhKzRTeyVr8siFCddDHpONOsY> : Exploit Protection)

              *            Safeguard 10.5: Enable Anti-Exploitation Features: Enable anti-exploitation features on enterprise assets and software, where possible, such as Microsoft? Data Execution Prevention (DEP), Windows? Defender Exploit Guard (WDEG), or Apple? System Integrity Protection (SIP) and Gatekeeper™.

*            Block execution of code on a system through application control, and/or script blocking. (M1038 <https://learn.cisecurity.org/e/799323/mitigations-M1038-/4w1hj1/2733627729/h/9-fk1zhPs62wccYt3ayhKzRTeyVr8siFCddDHpONOsY> : <https://learn.cisecurity.org/e/799323/mitigations-M1038-/4w1hj1/2733627729/h/9-fk1zhPs62wccYt3ayhKzRTeyVr8siFCddDHpONOsY>  Execution Prevention)

              *            Safeguard 2.5: Allowlist Authorized Software: Use technical controls, such as application allowlisting, to ensure that only authorized software can execute or be accessed. Reassess bi-annually, or more frequently.

              *            Safeguard 2.6: Allowlist Authorized Libraries: Use technical controls to ensure that only authorized software libraries, such as specific .dll, .ocx, .so, etc., files, are allowed to load into a system process. Block unauthorized libraries from loading into a system process. Reassess bi-annually, or more frequently.

              *            Safeguard 2.7: Allowlist Authorized Scripts: Use technical controls, such as digital signatures and version control, to ensure that only authorized scripts, such as specific .ps1, .py, etc., files, are allowed to execute. Block unauthorized scripts from executing. Reassess bi-annually, or more frequently.

*            Use capabilities to prevent suspicious behavior patterns from occurring on endpoint systems. This could include suspicious process, file, API call, etc. behavior. (M1040: <https://learn.cisecurity.org/e/799323/mitigations-M1040-/4w1hj4/2733627729/h/9-fk1zhPs62wccYt3ayhKzRTeyVr8siFCddDHpONOsY>  Behavior Prevention on Endpoint)

              *            Safeguard 13.2: Deploy a Host-Based Intrusion Detection Solution: Deploy a host-based intrusion detection solution on enterprise assets, where appropriate and/or supported.

              *            Safeguard 13.7: Deploy a Host-Based Intrusion Prevention Solution: Deploy a host-based intrusion prevention solution on enterprise assets, where appropriate and/or supported. Example implementations include use of an Endpoint Detection and Response (EDR) client or host-based IPS agent.

REFERENCES:

              Adobe:

https://helpx.adobe.com/security/Home.html

https://helpx.adobe.com/security/products/formatplugins/apsb26-87.html

https://helpx.adobe.com/security/products/bridge/apsb26-89.html

              CVE:

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-48372

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-48374

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-48390

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-48391

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-48392

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-48393

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-48394

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-48395

https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-48396
Large-Scale Exploitation Campaign Targeting Website Content Management Systems

This Australian Signals Directorate (ASD) Australian Cyber Security Centre (ACSC) Alert is relevant to website owners and website managers. It is being provided to assist agencies and organizations in guarding against the persistent malicious actions of cybercriminals.

A large-scale exploitation campaign is targeting various vulnerabilities in content management systems (CMS) globally, including in Australia, with many small to medium sized Australian businesses impacted.

As part of this campaign, malicious cyber actors are actively scanning websites for opportunities to deploy webshells, leveraging various vulnerabilities affecting CMS software and plugins. These vulnerabilities primarily allow unauthenticated file upload, remote code execution, server side request forgery or deserialization.

Once deployed, webshells can allow malicious cyber actors to remotely access and control targeted web servers. Malicious cyber actors may leverage compromised web servers for several purposes, including:

• Website defacement or disruption
• Capturing credentials entered by website users or other data stored on web servers
• Uploading additional malware to target and scam legitimate website users
• Using web server access as a pathway for broader network compromise
This highly scaled global exploitation campaign demonstrates the rapidly evolving cyber risk facing organizations. The heads of the Five Eyes cyber security agencies recently released a joint statement highlighting how advances in AI are accelerating the speed and scale of cyber operations, reducing the time between vulnerability disclosure and exploitation

ASD’s ACSC recommends that website owners confirm whether their servers have been impacted and remediate accordingly.

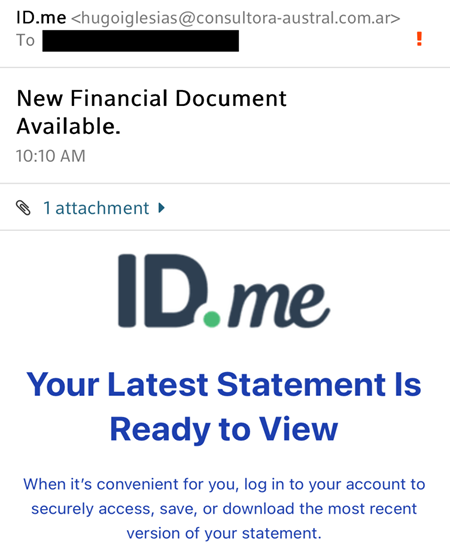
ID.me Phishing Campaign

The NJCCIC received reports of a phishing campaign impersonating ID.me, which is a US-based digital identity network that allows users to provide proof of their legal identity online to access government services, healthcare portals, and retailer discounts. The phishing email is sent from a “.ar” top-level domain (TLD) for Argentina with a subject line of “New Financial Document Available.” It contains an attachment and link that, if clicked, directs users to a phishing website to set up an ID.me account. The website requests personal information, such as home address, phone number, and Social Security number. It also requires the user to upload a valid, government-issued photo identification, such as a driver’s license or passport. If submitted, the information is sent to the threat actors in the background to commit identity theft and fraud.
Recommendations
Exercise caution with communications from known senders or legitimate services or platforms.

Confirm requests from senders using contact information obtained from verified, official sources before taking action, such as clicking links, opening attachments, and providing personal or financial information.

Navigate directly to the legitimate ID.me website and review their FAQs.

Enable multi-factor authentication (MFA) and keep systems and browsers up to date.

If sensitive information was submitted, review the Identity Theft and Compromised PII NJCCIC Informational Report for additional recommendations and resources. Report malicious cyber activity to the NJCCIC and the FBI’s IC3.

Understanding Browser Push Notifications:A Gateway to Online Scams

Websites often ask for permission to send you “push notifications.” When used correctly, this feature is highly convenient. If you use a communication tool like Microsoft Teams or a news website in your browser, a small pop-up in the corner of your screen can alert you to a new message or breaking news, even if that specific window is minimized. Unfortunately, cybercriminals frequently abuse this same feature to launch deceptive scam campaigns.
The Illusion of Danger vs. Actual Threats
It is critical to understand how these scams operate. The most important takeaway is that seeing a scary pop-up notification does not mean your computer is infected.
When a malicious or compromised website tricks you into allowing notifications, it gains the ability to send text and images directly to your desktop. Scammers use this to create fake alerts that look identical to official anti-virus warnings, system errors, or security breaches. They may claim your machine is compromised, your subscription has expired, or urgent action is required.
At their mildest, these notifications are a nuisance; they flood your screen with unwanted advertisements and consume your computer’s memory (RAM), which can slow down your system. At their worst, they leverage fear to create a threat where none yet exists.
How the Trap Snares Users
The notification itself cannot harm your computer or steal your data. The danger only begins if you interact with it.
The goal of the scammer is to scare you into taking one of two actions:
Clicking the notification: When you click the alert, it opens your web browser and often directs you to a malicious website (or redirects you through a chain of hidden sites). Once there, the site uses aggressive scare tactics, such as fake progress bars, flashing red screens, or countdown timers to coerce and pressure you into clicking a link that downloads actual malware onto your device. Calling a phone number: The alert may provide a fake “IT Support” or “Help Desk” number. If you call, a scammer will use social engineering tactics to trick you into handing over passwords, financial information, or granting them remote access to your computer.
Spotting the Fake: Check the Source
Because scammers are highly skilled at making their alerts look like official Windows or Mac system warnings, you cannot rely on the logos or the text inside the pop-up to determine if it is real. Instead, look at the notification envelope. Every browser push notification must be displayed by the computer’s operating system with its true origin.
When an alert pops up in the corner of your screen, look closely at the very top or bottom edge of the notification box. You will see two telltale signs:
The Browser Icon: You will see a tiny icon for Google Chrome, Microsoft Edge, or Mozilla Firefox. A real anti-virus program or Windows system update will never appear inside a browser window or carry a browser logo. The Website Domain: You will see the exact web address (for example: best-cleaner-source[.]xyz or prizes-winner[.]net) that is sending the message.
If a concerning notification claims your computer is infected with 15 viruses, but the small print at the edge of the box says it is coming from an unfamiliar website address via “Google Chrome,” you are looking at a bluff. A website cannot scan your computer’s hard drive.
How to Protect Yourself
The most effective defense against this tactic is awareness. By recognizing that these pop-ups are website messages rather than actual system diagnoses, you eliminate the scammer’s primary weapon: panic.
If you are already receiving these disruptive alerts, you can easily stop them. You do not need expensive software to fix this; you simply need to revoke the website’s permission within your internet browser.
Whether you use Google Chrome, Microsoft Edge, Safari, or Mozilla Firefox, the process is straightforward:
Open Browser Settings: All Browsers. Click the three dots or lines in the top-right corner of your browser and select Settings. Navigate to Site Permissions: Privacy & Security. Look for a section labeled Privacy and Security or Cookies and Site Permissions, then click on Notifications. Review the Allowed List: Identify the Culprit. Scroll down to the “Allow” or “Allowed to send notifications” list. Look for any website names you do not recognize or that seem suspicious. Remove or Block: Stop the Alerts. Click the three dots next to the suspicious website and choose Remove or Block. This instantly revokes its ability to send pop-ups to your desktop.
Tip: To prevent this from happening in the future, you can go to your browser’s notification settings and toggle the option to “Don’t allow sites to send notifications.” This will stop websites from even asking for permission and, instead, block the scam at the front door.

Improve Router Hygiene to Protect Against Russian State-Sponsored Targeting

United States Federal and international partner agencies, released this Joint Cybersecurity Advisory to provide network defenders with vital tools and resources to combat the threat posed by Russian Government-sponsored activity targeting poorly configured and vulnerable devices across critical sectors.
Russian Federal Security Service (FSB) Center 16 cyber actors continue to exploit poorly configured and vulnerable networking devices worldwide, opportunistically compromising multiple critical infrastructure sector networks. This Joint Cybersecurity Advisory builds on FBI’s Russian Government Cyber Actors Targeting Networking Devices, Critical Infrastructure Public Service Announcement of the decade plus FSB Center 16 cyber activity by providing additional tactics, techniques, and procedures (TTPs) to enable defenders to more fully understand and counter the threat.
The authoring and co-sealing agencies strongly urge device owners and network defenders to take mitigation and remediation actions against Russian government-sponsored exploitation of vulnerable routers.

Trusted Technologies Create Pathways Into Critical Infrastructure Networks

Critical infrastructure organizations are increasingly dependent on third-party vendors for a variety of remote services, including security and operational technologies that support essential functions. Yet the privileged access that providers rely on can also create opportunities for threat actors to infiltrate these sensitive networks. Recent incidents involving Itron and Fortinet illustrate how trusted relationships can create exposure through both compromises, affecting customer environments and compromised credentials for devices at the network perimeter.
In April, Itron disclosed that threat actors obtained unauthorized access to its systems. The company further identified limited unauthorized access to some customer-hosted systems; however, an investigation found no evidence that customer-facing system functionality was meaningfully impacted. Itron supplies technology that energy and water utilities use to measure resource usage and communicate with devices across their service networks. Although the company has not publicly stated how threat actors gained initial access or what information they obtained, the incident shows how a compromise of a trusted technology provider can also expose customer-managed environments across multiple critical infrastructure organizations. This exposure could also create a foothold for credential theft, lateral movement, or attempts to reach systems that support essential services.
In June, researchers identified a large-scale credential compromise campaign known as FortiBleed, illustrating a different form of exposure. The campaign involved credentials for more than 70,000 internet-facing Fortinet devices, potentially enabling access to customer-operated firewalls and VPN gateways. According to Fortinet , some of the exposed credentials were likely obtained during earlier incidents, while others may have been compromised through brute-force activity against devices with weak passwords and no multi-factor authentication (MFA) enabled. The company said the activity was not tied to a newly identified product vulnerability. Fortinet firewalls and virtual private network gateways often control remote access at the network perimeter. Valid credentials could therefore grant threat actors entry into customer environments and an opportunity to weaken security controls or move further into internal networks. This creates particular concern for energy and water organizations that rely on these devices for employee and vendor access.
Recommendations
Inventory third-party services, vendor accounts, remote-access pathways, and internet-facing devices with access to sensitive environments.
Limit vendor and administrative access to only the systems, users, and time periods required, and periodically remove unused accounts and unnecessary privileges.
Require multi-factor authentication (MFA) for remote and privileged access, where possible, and use strong, unique passwords across devices and accounts.
Rotate credentials following suspected exposure and terminate active sessions when a compromise is identified.
Restrict management interfaces from public internet access, segment remote-access services from sensitive business and operational technology environments, and replace unsupported devices.
Review firewall, virtual private network (VPN), authentication, and vendor-access logs for unusual login attempts, configuration changes, or newly created accounts.