Large-Scale Exploitation Campaign Targeting Website Content Management Systems

This Australian Signals Directorate (ASD) Australian Cyber Security Centre (ACSC) Alert is relevant to website owners and website managers. It is being provided to assist agencies and organizations in guarding against the persistent malicious actions of cybercriminals.

A large-scale exploitation campaign is targeting various vulnerabilities in content management systems (CMS) globally, including in Australia, with many small to medium sized Australian businesses impacted.

As part of this campaign, malicious cyber actors are actively scanning websites for opportunities to deploy webshells, leveraging various vulnerabilities affecting CMS software and plugins. These vulnerabilities primarily allow unauthenticated file upload, remote code execution, server side request forgery or deserialization.

Once deployed, webshells can allow malicious cyber actors to remotely access and control targeted web servers. Malicious cyber actors may leverage compromised web servers for several purposes, including:

• Website defacement or disruption
• Capturing credentials entered by website users or other data stored on web servers
• Uploading additional malware to target and scam legitimate website users
• Using web server access as a pathway for broader network compromise
This highly scaled global exploitation campaign demonstrates the rapidly evolving cyber risk facing organizations. The heads of the Five Eyes cyber security agencies recently released a joint statement highlighting how advances in AI are accelerating the speed and scale of cyber operations, reducing the time between vulnerability disclosure and exploitation

ASD’s ACSC recommends that website owners confirm whether their servers have been impacted and remediate accordingly.
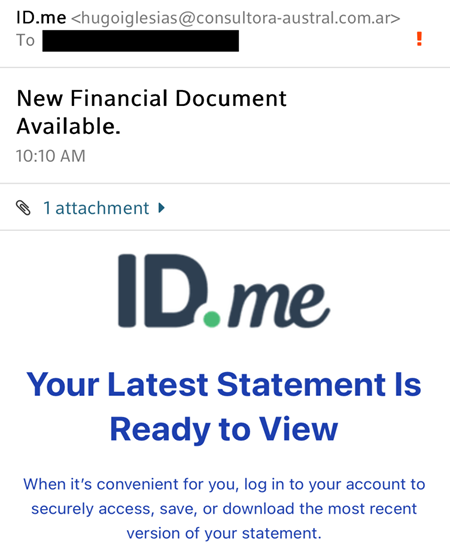
ID.me Phishing Campaign

The NJCCIC received reports of a phishing campaign impersonating ID.me, which is a US-based digital identity network that allows users to provide proof of their legal identity online to access government services, healthcare portals, and retailer discounts. The phishing email is sent from a “.ar” top-level domain (TLD) for Argentina with a subject line of “New Financial Document Available.” It contains an attachment and link that, if clicked, directs users to a phishing website to set up an ID.me account. The website requests personal information, such as home address, phone number, and Social Security number. It also requires the user to upload a valid, government-issued photo identification, such as a driver’s license or passport. If submitted, the information is sent to the threat actors in the background to commit identity theft and fraud.
Recommendations
Exercise caution with communications from known senders or legitimate services or platforms.

Confirm requests from senders using contact information obtained from verified, official sources before taking action, such as clicking links, opening attachments, and providing personal or financial information.

Navigate directly to the legitimate ID.me website and review their FAQs.

Enable multi-factor authentication (MFA) and keep systems and browsers up to date.

If sensitive information was submitted, review the Identity Theft and Compromised PII NJCCIC Informational Report for additional recommendations and resources. Report malicious cyber activity to the NJCCIC and the FBI’s IC3.

Understanding Browser Push Notifications:A Gateway to Online Scams

Websites often ask for permission to send you “push notifications.” When used correctly, this feature is highly convenient. If you use a communication tool like Microsoft Teams or a news website in your browser, a small pop-up in the corner of your screen can alert you to a new message or breaking news, even if that specific window is minimized. Unfortunately, cybercriminals frequently abuse this same feature to launch deceptive scam campaigns.
The Illusion of Danger vs. Actual Threats
It is critical to understand how these scams operate. The most important takeaway is that seeing a scary pop-up notification does not mean your computer is infected.
When a malicious or compromised website tricks you into allowing notifications, it gains the ability to send text and images directly to your desktop. Scammers use this to create fake alerts that look identical to official anti-virus warnings, system errors, or security breaches. They may claim your machine is compromised, your subscription has expired, or urgent action is required.
At their mildest, these notifications are a nuisance; they flood your screen with unwanted advertisements and consume your computer’s memory (RAM), which can slow down your system. At their worst, they leverage fear to create a threat where none yet exists.
How the Trap Snares Users
The notification itself cannot harm your computer or steal your data. The danger only begins if you interact with it.
The goal of the scammer is to scare you into taking one of two actions:
Clicking the notification: When you click the alert, it opens your web browser and often directs you to a malicious website (or redirects you through a chain of hidden sites). Once there, the site uses aggressive scare tactics, such as fake progress bars, flashing red screens, or countdown timers to coerce and pressure you into clicking a link that downloads actual malware onto your device. Calling a phone number: The alert may provide a fake “IT Support” or “Help Desk” number. If you call, a scammer will use social engineering tactics to trick you into handing over passwords, financial information, or granting them remote access to your computer.
Spotting the Fake: Check the Source
Because scammers are highly skilled at making their alerts look like official Windows or Mac system warnings, you cannot rely on the logos or the text inside the pop-up to determine if it is real. Instead, look at the notification envelope. Every browser push notification must be displayed by the computer’s operating system with its true origin.
When an alert pops up in the corner of your screen, look closely at the very top or bottom edge of the notification box. You will see two telltale signs:
The Browser Icon: You will see a tiny icon for Google Chrome, Microsoft Edge, or Mozilla Firefox. A real anti-virus program or Windows system update will never appear inside a browser window or carry a browser logo. The Website Domain: You will see the exact web address (for example: best-cleaner-source[.]xyz or prizes-winner[.]net) that is sending the message.
If a concerning notification claims your computer is infected with 15 viruses, but the small print at the edge of the box says it is coming from an unfamiliar website address via “Google Chrome,” you are looking at a bluff. A website cannot scan your computer’s hard drive.
How to Protect Yourself
The most effective defense against this tactic is awareness. By recognizing that these pop-ups are website messages rather than actual system diagnoses, you eliminate the scammer’s primary weapon: panic.
If you are already receiving these disruptive alerts, you can easily stop them. You do not need expensive software to fix this; you simply need to revoke the website’s permission within your internet browser.
Whether you use Google Chrome, Microsoft Edge, Safari, or Mozilla Firefox, the process is straightforward:
Open Browser Settings: All Browsers. Click the three dots or lines in the top-right corner of your browser and select Settings. Navigate to Site Permissions: Privacy & Security. Look for a section labeled Privacy and Security or Cookies and Site Permissions, then click on Notifications. Review the Allowed List: Identify the Culprit. Scroll down to the “Allow” or “Allowed to send notifications” list. Look for any website names you do not recognize or that seem suspicious. Remove or Block: Stop the Alerts. Click the three dots next to the suspicious website and choose Remove or Block. This instantly revokes its ability to send pop-ups to your desktop.
Tip: To prevent this from happening in the future, you can go to your browser’s notification settings and toggle the option to “Don’t allow sites to send notifications.” This will stop websites from even asking for permission and, instead, block the scam at the front door.

Improve Router Hygiene to Protect Against Russian State-Sponsored Targeting

United States Federal and international partner agencies, released this Joint Cybersecurity Advisory to provide network defenders with vital tools and resources to combat the threat posed by Russian Government-sponsored activity targeting poorly configured and vulnerable devices across critical sectors.
Russian Federal Security Service (FSB) Center 16 cyber actors continue to exploit poorly configured and vulnerable networking devices worldwide, opportunistically compromising multiple critical infrastructure sector networks. This Joint Cybersecurity Advisory builds on FBI’s Russian Government Cyber Actors Targeting Networking Devices, Critical Infrastructure Public Service Announcement of the decade plus FSB Center 16 cyber activity by providing additional tactics, techniques, and procedures (TTPs) to enable defenders to more fully understand and counter the threat.
The authoring and co-sealing agencies strongly urge device owners and network defenders to take mitigation and remediation actions against Russian government-sponsored exploitation of vulnerable routers.

Trusted Technologies Create Pathways Into Critical Infrastructure Networks

Critical infrastructure organizations are increasingly dependent on third-party vendors for a variety of remote services, including security and operational technologies that support essential functions. Yet the privileged access that providers rely on can also create opportunities for threat actors to infiltrate these sensitive networks. Recent incidents involving Itron and Fortinet illustrate how trusted relationships can create exposure through both compromises, affecting customer environments and compromised credentials for devices at the network perimeter.
In April, Itron disclosed that threat actors obtained unauthorized access to its systems. The company further identified limited unauthorized access to some customer-hosted systems; however, an investigation found no evidence that customer-facing system functionality was meaningfully impacted. Itron supplies technology that energy and water utilities use to measure resource usage and communicate with devices across their service networks. Although the company has not publicly stated how threat actors gained initial access or what information they obtained, the incident shows how a compromise of a trusted technology provider can also expose customer-managed environments across multiple critical infrastructure organizations. This exposure could also create a foothold for credential theft, lateral movement, or attempts to reach systems that support essential services.
In June, researchers identified a large-scale credential compromise campaign known as FortiBleed, illustrating a different form of exposure. The campaign involved credentials for more than 70,000 internet-facing Fortinet devices, potentially enabling access to customer-operated firewalls and VPN gateways. According to Fortinet , some of the exposed credentials were likely obtained during earlier incidents, while others may have been compromised through brute-force activity against devices with weak passwords and no multi-factor authentication (MFA) enabled. The company said the activity was not tied to a newly identified product vulnerability. Fortinet firewalls and virtual private network gateways often control remote access at the network perimeter. Valid credentials could therefore grant threat actors entry into customer environments and an opportunity to weaken security controls or move further into internal networks. This creates particular concern for energy and water organizations that rely on these devices for employee and vendor access.
Recommendations
Inventory third-party services, vendor accounts, remote-access pathways, and internet-facing devices with access to sensitive environments.
Limit vendor and administrative access to only the systems, users, and time periods required, and periodically remove unused accounts and unnecessary privileges.
Require multi-factor authentication (MFA) for remote and privileged access, where possible, and use strong, unique passwords across devices and accounts.
Rotate credentials following suspected exposure and terminate active sessions when a compromise is identified.
Restrict management interfaces from public internet access, segment remote-access services from sensitive business and operational technology environments, and replace unsupported devices.
Review firewall, virtual private network (VPN), authentication, and vendor-access logs for unusual login attempts, configuration changes, or newly created accounts.

Passkeys by default and retirement of Microsoft-provided SMS and voice authentication

Move to phishing-resistant authentication before SMS and voice retire

We are notifying all Microsoft Entra ID tenants of an important change to authentication security: The AI era demands stronger, phishing-resistant authentication. Passkeys are becoming the default authentication experience in Microsoft Entra, and Microsoft-provided SMS and voice authentication will retire on February 1, 2027.

For more context on why Microsoft is moving to phishing-resistant authentication by default, please read our Microsoft Security Blog announcement.

What is changing

  • Passkeys become the default authentication experience for users currently enabled for SMS or voice.
  • Microsoft-provided telecom delivery for SMS and voice will be retired. Customer-managed telecom providers configured through the Microsoft Security Store are not affected.

Why this is changing

SMS and voice are among the most vulnerable authentication methods available today and provide significantly weaker protection against phishing, SIM-swap, and replay attacks than passkeys. Moving to phishing-resistant methods gives your organization stronger security by default.

Impact on you and key dates

  • September 1, 2026 — Users enabled for SMS or voice are automatically enabled for passkeys and will be nudged to register a passkey when they next complete MFA. (If you do not want this, move users out of SMS or voice in the Authentication Methods Policy before this date.)
  • February 1, 2027 — Microsoft-provided SMS and voice are fully retired in Microsoft Entra ID. Customer-managed telecom providers are unaffected.
  • After February 1, 2027 — Users whose only available MFA method is SMS or voice will receive a blocking prompt to register a passkey before they can continue signing in. There is no opt out from this enforcement; it applies to all tenants.

If no users in your tenant are enabled for SMS or voice, no action is required and you can disregard the steps below.

If you do have users enabled for SMS or voice, the required action is to move every one of those users off SMS and voice before February 1, 2027. Microsoft recommends passkeys — the default phishing-resistant credential in Microsoft Entra ID. Take the following steps:

  1. Find affected users. Identify who in your tenant is still enabled for SMS or voice.
  2. Move users to passkeys. Enable passkeys and run a registration campaign to drive adoption at scale before auto-enablement on September 1, 2026.
  3. Communicate the change. Notify your users of what is changing, when, and the action they need to take.
  4. Evaluate a telecom provider only if required. If you have a regulatory or operational need to keep SMS or voice, configure a customer-managed provider through the Microsoft Security Store before February 1, 2027 (provider options and pricing published beginning September 18, 2026; configuration available beginning October 30, 2026).

The bottom line: every SMS and voice user must be on a phishing-resistant method — passkeys are recommended — before Microsoft-provided SMS and voice retire on February 1, 2027. Acting before September 1, 2026 lets you move users on your own schedule and avoid blocking prompts.

       Read migration guidance >       

Isolating Vital Operational Technology and Enabling Systems During Crisis

The Cybersecurity and Infrastructure Security Agency (CISA) and the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC), in collaboration with the Federal Bureau of Investigation (FBI) and international partners, published Joint Guidance CI Fortify – Advice for isolating vital systems. This guidance, aligned with CISA’s CI Fortify initiative, is designed to help critical infrastructure (CI) owners and operators prepare to isolate their operational technology (OT) and enabling systems to maintain essential operations during a significant cybersecurity incident or crisis.
State-sponsored cyber threat actors are increasingly targeting critical infrastructure for pre-positioning. By physically isolating vital OT and enabling systems, CI operators and defenders can disrupt adversaries, contain attacks in progress, and rebuild compromised systems.
This Joint Guidance provides practical steps for isolating vital systems, such as identifying and mapping critical assets and connections, building effective separation points, and developing graduated isolation plans with regular testing. The guidance also outlines temporary measures to support network isolation for organizations unable to physically isolate, while emphasizing that physical isolation remains the most risk-effective solution.
Read the isolation guidance to learn more. Visit the CI Fortify webpage for additional resources on CI security and resilience.

Building Assurance Through HIPAA Security Conference

The U.S. Department of Health and Human Services Office for Civil Rights (OCR) and the National Institute of Standards and Technology (NIST) Information Technology Laboratory (ITL) are excited to announce their 2026 Conference, “Safeguarding Health Information: Building Assurance Through HIPAA Security 2026”.

DATES: September 2 – 3, 2026

LOCATION: NIST Gaithersburg Campus, 100 Bureau Drive, Gaithersburg, MD, 20899

CONTENT: The conference will include panels and presentations addressing a variety of topics including practical strategies, tips and techniques for implementing the Health Insurance Portability and Accountability Act of 1996 (HIPAA) Security Rule, managing cybersecurity risk and implementing practical cybersecurity solutions, understanding current cybersecurity threats to the healthcare community, updates from federal healthcare agencies, cybersecurity considerations when adopting new technologies, and more.

Registration for the event is now open for both in-person and virtual attendance.

Please visit the event web page for more details and to register for the conference.

Hope to see you there!

Register Today! NIST Workshop | Securing AI Data Center: Architecture, Security Posture, and Emerging Standards

Securing AI Data Center: Architecture, Security Posture, and Emerging Standards Workshop Remember to register for the Secure AI Data Center Workshop before Tuesday, July 21, 2026. The agenda is now available. Data centers are the computing infrastructure that powers the training and inference of artificial intelligence (AI), and they have become a critical element of national security, economic strength, and technological dominance. To address the urgent need for robust technical standards outlined in America’s AI Action Plan, NIST (ITL, CAISI) and the DoW High-Performance Computing Modernization Program (HPCMP) are proud to host the virtual workshop, “Securing AI Data Center: Architecture, Security Posture, and Emerging Standards,” on July 22-23, 2026. This two-day event will bring together stakeholders from government, industry, and academia to collaborate on the future of AI data center security. Critical topics will include hardware and software architecture, physical and personnel security, regulatory compliance, and supply chain resilience. The community of interest is invited to help define future directions, review ongoing NIST activities, and establish the security posture necessary for protecting next-generation AI infrastructure.

Register today to join the workshop and help shape emerging standards.

Register Now NIST Cybersecurity and Privacy Program
CSRC Website questions: csrc-inquiry@nist.gov

Security Guidelines for Storage Infrastructure: Draft SP 800-209r1 Available for Public Comment

The initial public draft (ipd) of NIST Special Publication (SP) 800-209r1, Security Guidelines for Storage Infrastructure, is now available for public comment.

Storage technology has evolved in two primary directions: (1) increased media storage capacity and (2) architectural changes that provide a software-based abstraction over all forms of background storage technologies. However, the latter evolution has increased management complexity and the probability of configuration errors and associated security threats. This document traces the evolution of the storage technology landscape and analyzes current security threats and resultant risks to provide a comprehensive set of security recommendations in the form of storage security controls.

The public comment period is open through September 8, 2026. See the publication details for a copy of the draft, instructions for submitting comments, and a summary of important changes in this revision.

NOTE: A call for patent claims is included in this draft. For additional information, see the Information Technology Laboratory (ITL) Patent Policy – Inclusion of Patents in ITL Publications.

Read More